Mender blog
On Oct 23rd 2026, from 13:45 to 15:01 UTC, our hosted Mender production instance was abused to send spam emails. It took us 1 hour and 16 minutes to detect the problem, disable email sending, find the offending user and suspend them to stop the abuse.
The spammer used Mender as a spam email service - they brought their own message and list of email addresses to send to. Mender users were not compromised or targeted or affected (aside from us turning off email sending for about 1 hour while handling the issue).
Timeline
| Time (UTC) | Event |
|---|---|
| 13:45 | Abusive invitations start. |
| 14:09 | Monitoring alert fired, notifying the operations team. |
| 14:37 | Alarm acknowledged, investigation started. |
| 14:46 | Status page incident created. |
| 14:54 | Email sending service (Amazon SES) suspended, stopping the abuse. |
| 15:01 | Offending tenant identified and suspended. |
| 15:13 | Stricter rate limit implemented and deployed for email invitations. |
| 16:05 | Updated email template to reduce the possibility for similar abuse. |
| 16:08 | Email sending re-enabled, status page updated. |
Description
The spammer put a long text inside their Mender organization name, with content intended to make the target call a US-based phone number, and started inviting users to this organization. This resulted in the invited users receiving an email like this:
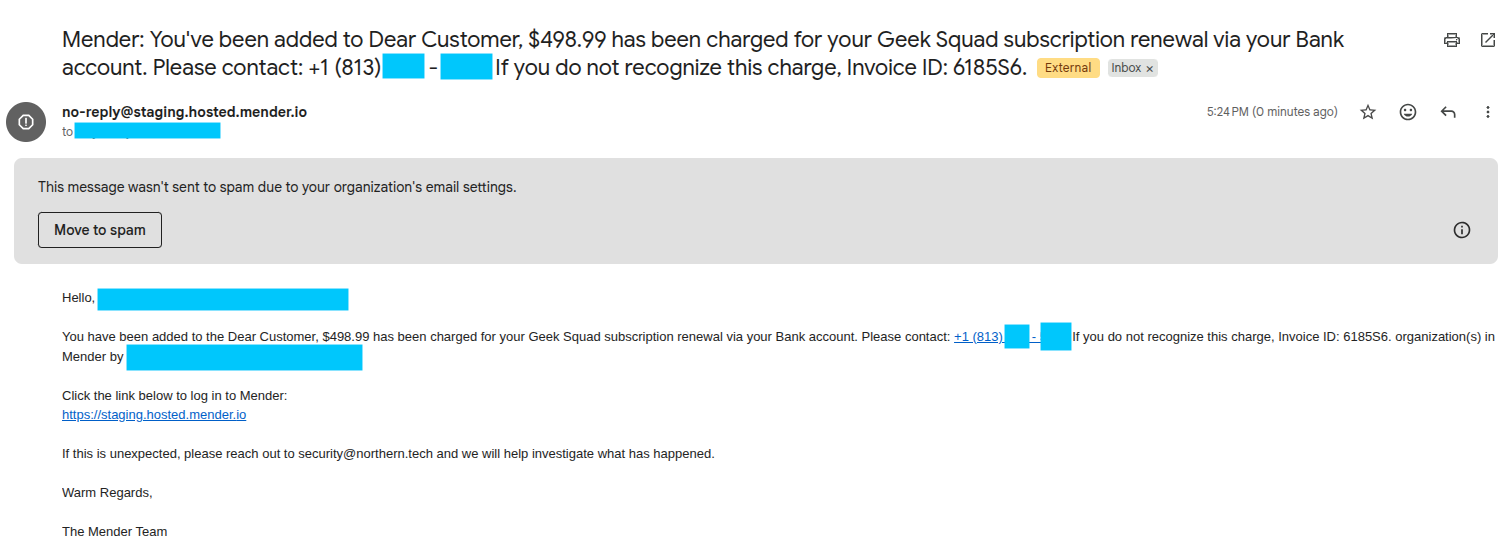
While it looks quite strange and not very convincing, it is possible that some small fraction of the users targeted by this might be tricked. The malicious actor attempted to invite 26 000 email addresses in this manner. A majority of the emails bounced or failed - around 8 000 emails succeeded. In our testing, we found that common email service providers like gmail.com does (correctly) mark this as spam - so the email above might go directly to the user's spam folder, and not be seen at all.
Follow-ups
Following the incident we have performed several actions, including:
- Contacting the ~8 000 affected recipients, telling them to ignore the previously received email address and beware of similar spam / scam attempts in the future. Their email addresses were already in a list used by the spammers, so it is likely they might be targeted again by similar spam in the future.
- Reporting the US phone number and email address to the US FTC (Report Fraud service).
- Adding stricter rate limits to make similar kinds of abuse much slower and more limited.
- Adjusting email templates to limit what information can be put inside them by users for these kinds of malicious purposes.
We will review our monitoring and alerting systems and consider what else we can do to improve and avoid similar situations in the future. We apologize for any inconvenience or confusion this incident may have caused you.
Recent articles
Achieving compliance and security for static medical devices
Discover how to ensure compliance and security for medical devices through effective software updates, addressing lifecycle challenges and regulatory demands.
Official release: New component orchestration offers system-level software updates to multi-component products in Mender
Component orchestration is now available in Mender, enabling coordinated system-level software updates across multiple components, ensuring seamless and robust updates for connected products.
Clarifications regarding recent PHP vulnerabilities (CVE-2026-109618 & CVE-2026-109619)
Statement regarding how the recent PHP vulnerabilities apply to Mender and its websites.
Learn why leading companies choose Mender
Discover how Mender empowers both you and your customers with secure and reliable over-the-air updates for IoT devices. Focus on your product, and benefit from specialized OTA expertise and best practices.